IT Audit: User Access Control Analysis
View on GitHubAudit & Risk
IT Audit: User Access Control Analysis
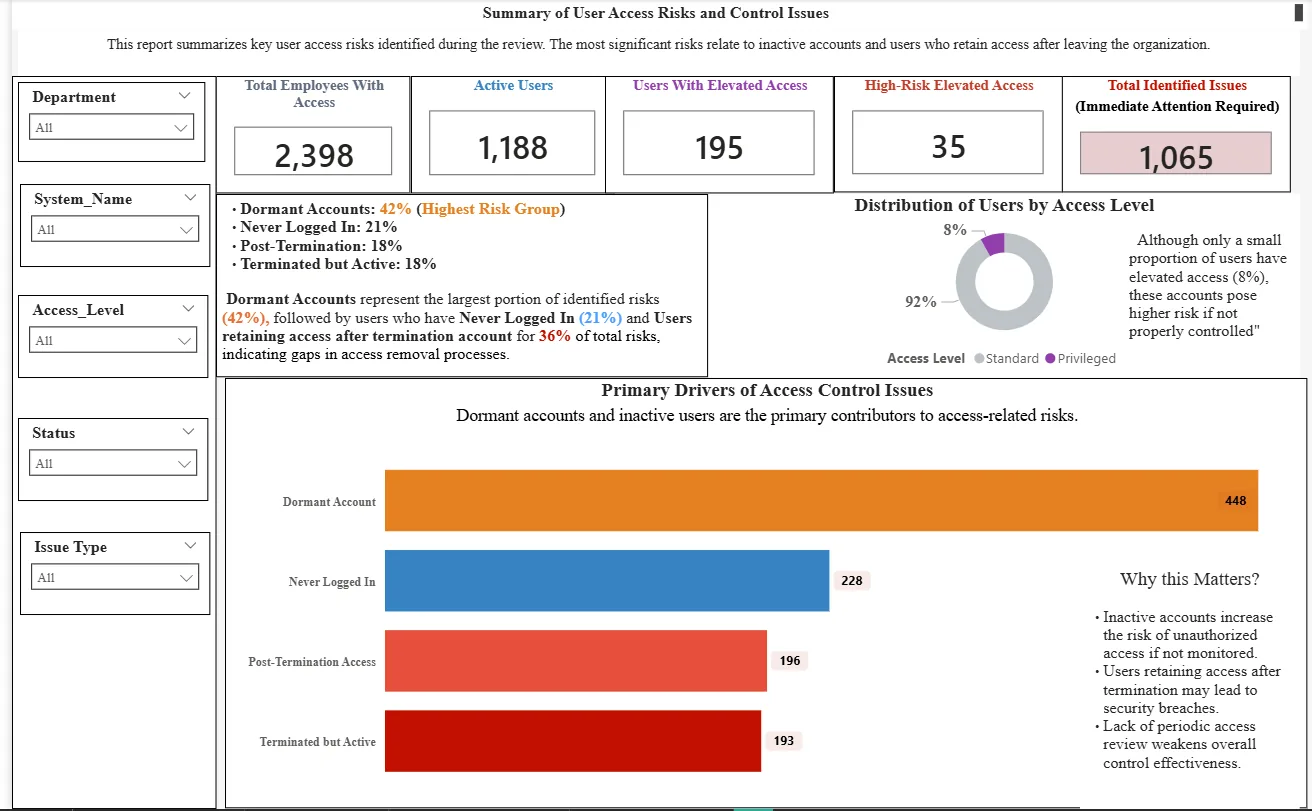
Full-population access-control testing across 2,398 accounts identified 1,065 exceptions (44.4%) across provisioning, deprovisioning, inactive accounts and privileged access.
Power BIDAXExcelRisk Matrix
Key Highlights
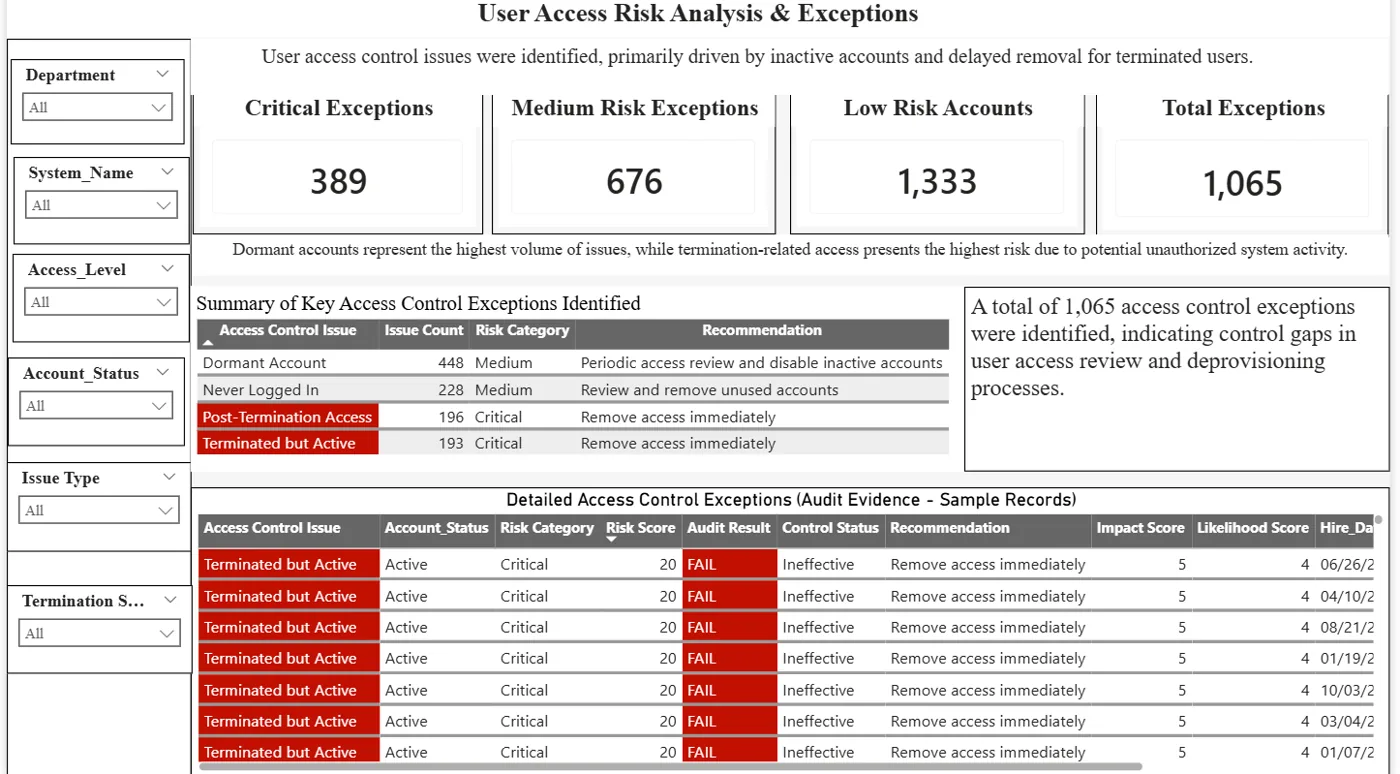
- 389 termination-related exceptions across post-termination access and accounts still active after termination.
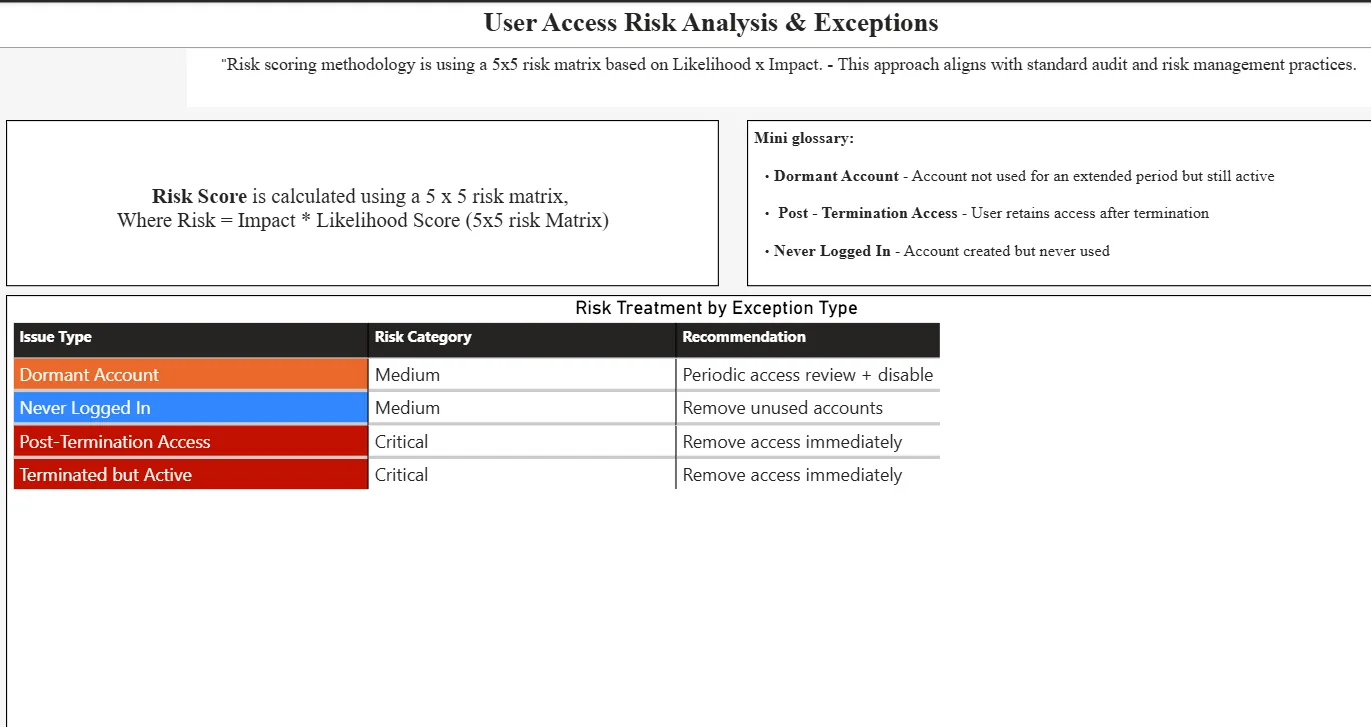
- Findings prioritized with a 5 × 5 Impact × Likelihood risk matrix.
- Four-page Power BI dashboard with DAX risk scoring and an exception register for audit evidence.
Tech Stack
Power BIDAXExcelRisk Matrix
Overview
An access-control review of a synthetic, anonymized account population. The analysis tests whether access was provisioned and removed appropriately, inactive accounts remained controlled, and privileged access was governed.
Methodology
- Tested 2,398 accounts across four control areas using full-population checks.
- Classified and risk-rated exceptions with a 5 × 5 Impact × Likelihood matrix.
- Presented the results in a four-page Power BI report with an auditable exception register.
Results & Findings
- 1,065 exceptions (44.4% of the tested population).
- 389 termination-related exceptions, including 196 post-termination and 193 active terminated accounts.
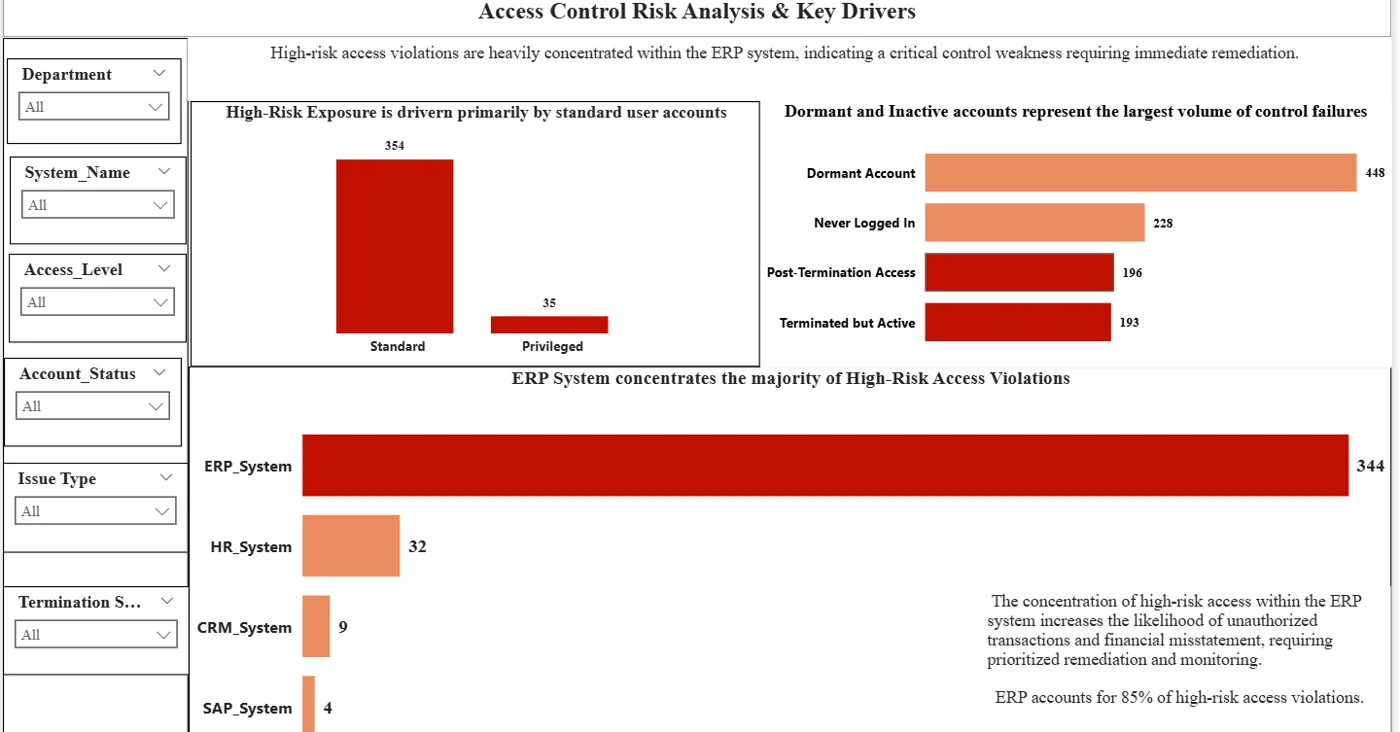
- Other recorded groups include 448 dormant and 228 never-logged-in accounts.
Getting Started
Open the Power BI report in Power BI Desktop. The repository describes synthetic, anonymized data.
git clone https://github.com/Jash275/IT-Audit-User-Access-Control-Analysis.git
# Open the .pbix report in Power BI Desktop
Screenshots